Form library · Quality and compliance
Security risk assessment template
For people assessing premises security arrangements. Record scope and assets, threat and vulnerability records and plan and governance. Try the form below, see every question or download a blank PDF or Word copy.
Ready to use from the form library, and every question is yours to edit. Trial from £1, cancel any time.
Try it on your phone
Try it on this phone
Fill in the physical security risk assessment on your phone now
See how the physical security risk assessment looks on your phone
Scan the code with your phone camera. It opens the real form, no sign-up needed.
Open the live example and fill it in, just as your team would on site. No sign-up needed.
See it on this phoneEvery question is editable. Add this form to your account, then change the wording, add or remove questions and options, and make it fit your own jobs.
What should a physical security assessment consider?
Protective security guidance takes a risk-based approach: understand what needs protection, the threats and vulnerabilities, and the measures needed to reduce risk. A site security plan should reflect the assessment and establish responsibilities and procedures.
Last updated . Facts checked by the SiteSurvey team on 6 October 2026 against ProtectUK security risk management and ProtectUK security planning and business continuity.
Try the physical security risk assessment form live
Answer a few questions and watch it adapt. Your answers are not saved, and any photos you add are deleted within the hour.
This is the real form as your team would use it: questions appear as you answer, scores work themselves out and you can add photos and signatures. No sign-up needed.
Want to see one filled in? See a completed physical security risk assessment report (PDF), made by SiteSurvey from a fictional site visit.
Fill it in on a phone or tablet
Your team completes the physical security risk assessment on site in the SiteSurvey app on iPhone, iPad and Android phones and tablets. The project name and address fill in for them, it works without signal, and it syncs when the device is back online with photos kept against the question they answer.
Customers and subcontractors do not need the app: send them a link and they can fill it in from any browser.
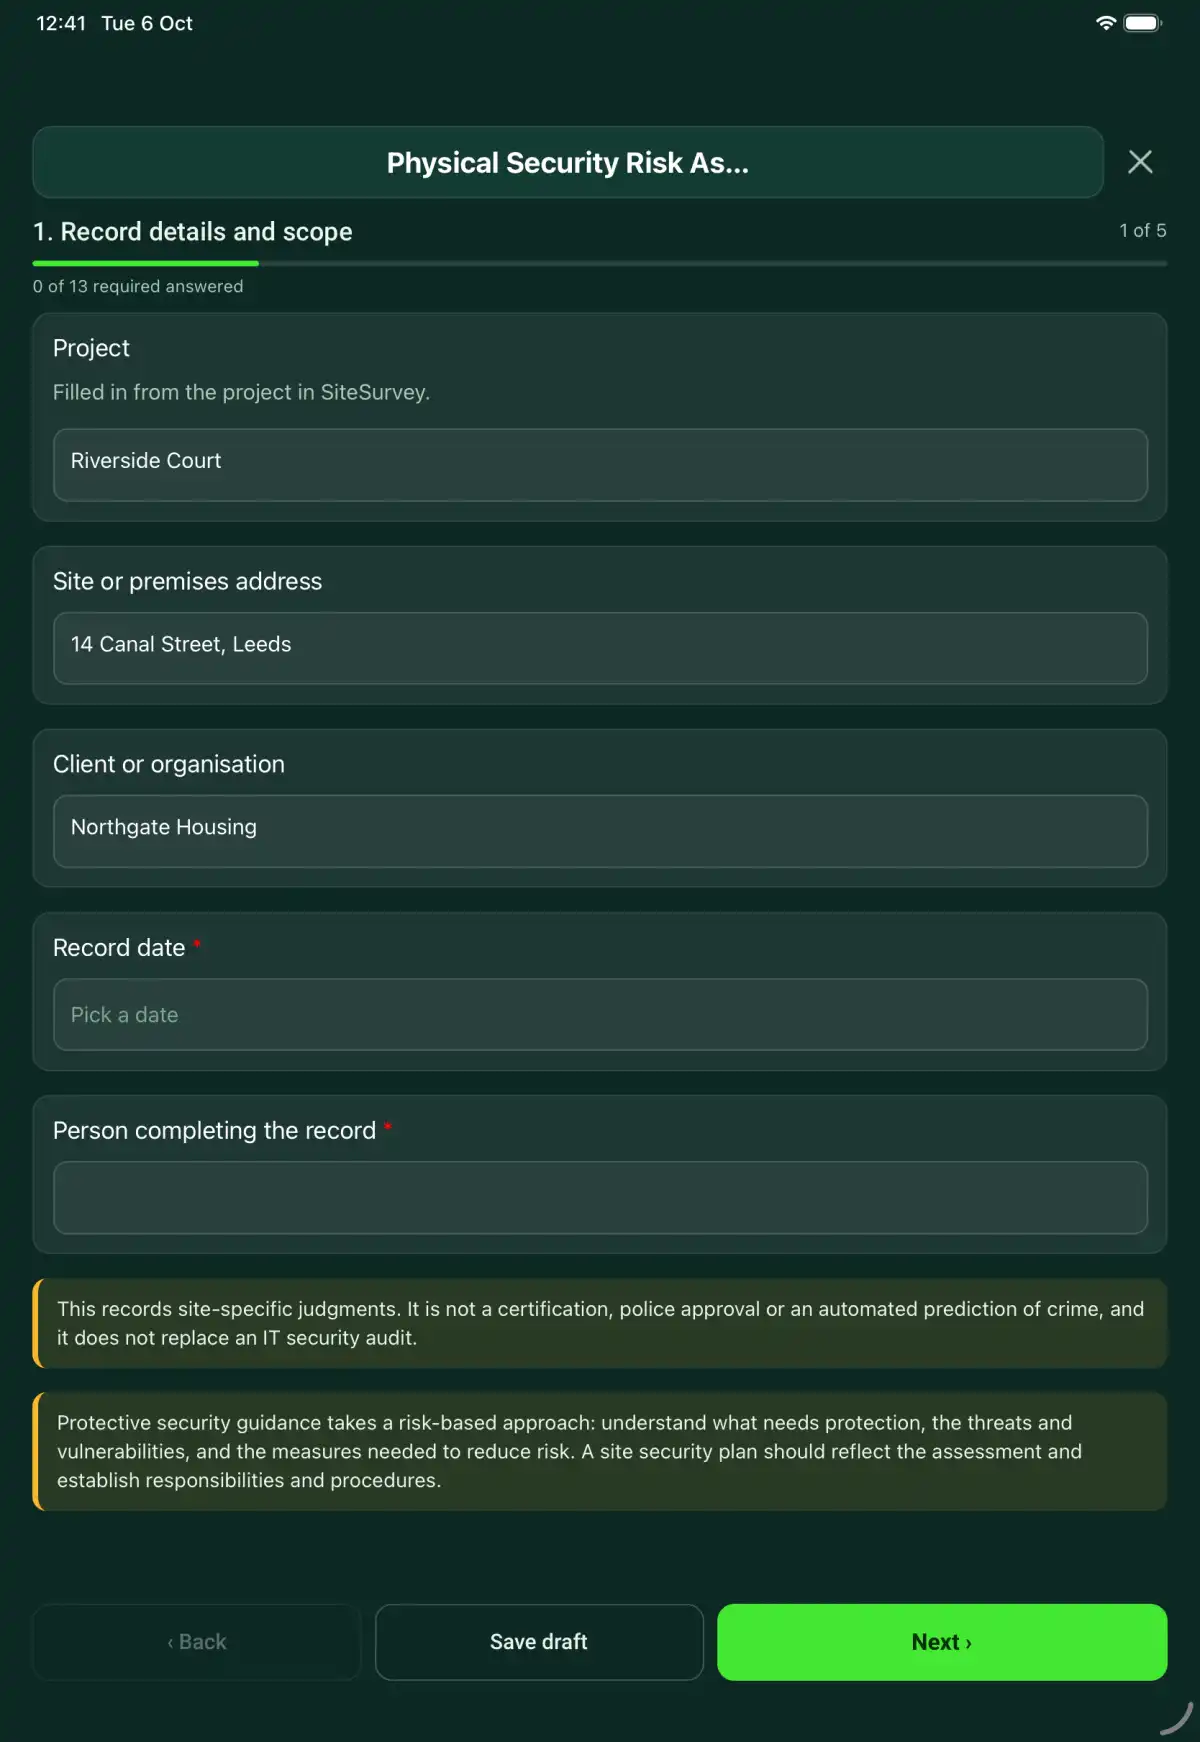
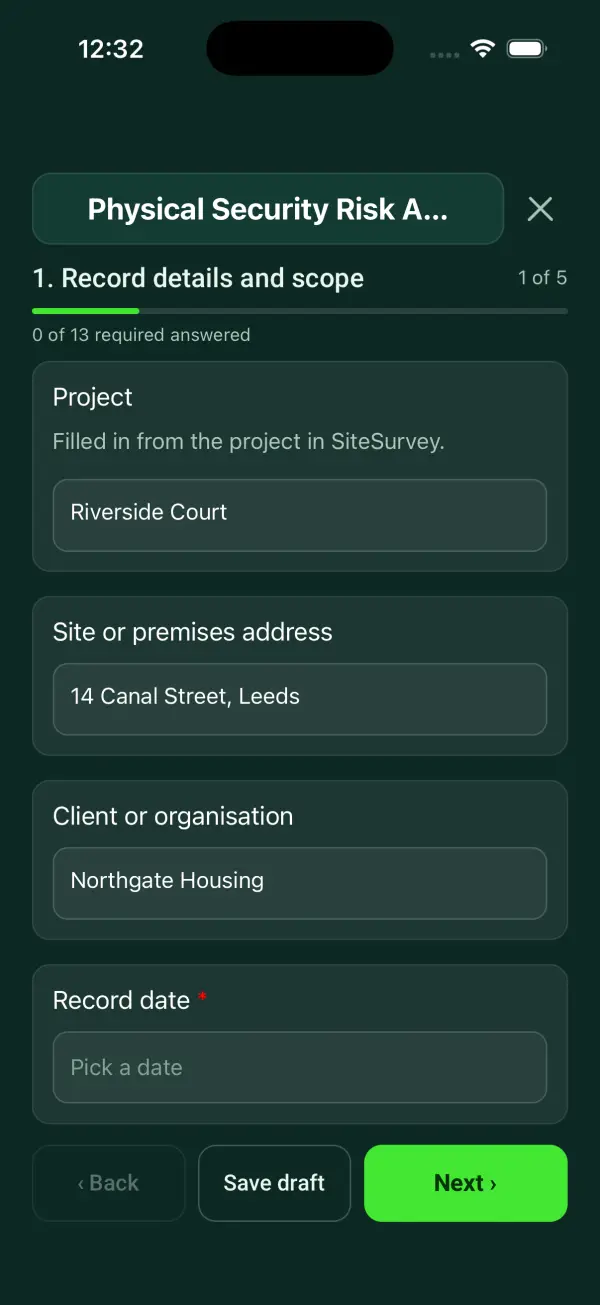
Every question in the physical security risk assessment template
A premises security assessment with assets, threats, vulnerabilities, existing controls, prioritised improvements and management review. 5 sections and 30 questions. Follow-up questions and guidance appear only when an answer calls for them, so the person on site never sees the ones that do not apply.
Make it your own: every question is editable
This is a starting point, not a fixed form. Once it is in your SiteSurvey account you can reword any question, add or remove questions, sections and answer options, and add your own logo, so it fits the way your team works and the jobs you do.
Details you only enter once
Add this form to a project in SiteSurvey and it fills in what the project already knows, so nobody on site retypes it and every form on the job uses the same names. Anything filled in can still be changed.
- Project: the project name
- Site or premises address: the site address, from the space or the project
- Client or organisation: the project's customer
Record details and scope
- ProjectShort answer
Filled in from the project in SiteSurvey.
Fills in from the project name - Site or premises addressShort answerFills in from the site address, from the space or the project
- Client or organisationShort answerFills in from the project's customer
- Record date*Date
- Person completing the record*Short answer
- CheckThis records site-specific judgments. It is not a certification, police approval or an automated prediction of crime, and it does not replace an IT security audit.
- CheckProtective security guidance takes a risk-based approach: understand what needs protection, the threats and vulnerabilities, and the measures needed to reduce risk. A site security plan should reflect the assessment and establish responsibilities and procedures.
Scope and assets
- Premises and activities included*Notes
- People, assets and operations needing protection*Notes
- Information sources, incidents and assumptionsNotes
- Assessment limits and sensitive information handlingNotes
State the areas, evidence and tests excluded from this assessment. Keep sensitive credentials out of the record.
Threat and vulnerability records
- Security riskRepeat for each security risk. Each one asks:
- Asset or location*Short answer
- Threat scenario and supporting information*Notes
- Vulnerability and existing controls*Notes
- Assessor priority*Choose one
- Immediate
- High
- Medium
- Low
- Reason for the priority and proposed improvement*Notes
Plan and governance
- Security roles, escalation and incident response*Notes
- Access, visitors, keys and contractor arrangementsNotes
- Changes and incidents triggering a reviewNotes
- Security plan referenceShort answer
- Manager reviewing the recommendationsShort answer
Actions and review
- Are further actions required?*Choose one
- Yes
- No
- Further actionRepeat for each further action. Each one asks:Shown when “Are further actions required?” is “Yes”
- Action and evidence reference*Notes
- Person responsible*Short answer
- Target dateDate
- Action status*Choose one
- Open
- In progress
- Completed
- Completion evidence*NotesShown when “Action status” is “Completed”
- Outstanding limitations and information to pass onNotes
- Record status*Choose one
- Ready for review
- Further work needed
- Work or use stopped
- Reviewed byShort answer
- Review dateDate
- Author signature*Signature
- CheckSigning records the information entered. It does not itself certify legal compliance, remove a limitation or authorise unsafe work.
Scope and responsibility
This records site-specific judgments. It is not a certification, police approval or an automated prediction of crime, and it does not replace an IT security audit.
What a useful entry looks like
Assessment limits and sensitive information handling
State the areas, evidence and tests excluded from this assessment. Keep sensitive credentials out of the record.
Review covers daytime reception access and the external perimeter. No alarm penetration testing was carried out and no access codes are recorded.
Fictional example of record wording. Use the actual evidence and approved arrangements for your job; this is not a completed report or an instruction to carry out the work.
See it filled in
A completed physical security risk assessment report, made by SiteSurvey from a fictional site visit: every answer, the photos, the guidance that applied and the sign-off, ready to send as a PDF.
Physical Security Risk Assessment FAQs
How should I record “Assessment limits and sensitive information handling”?
State the areas, evidence and tests excluded from this assessment. Keep sensitive credentials out of the record.
Does it calculate a risk score?
No. The assessor selects a priority and records a rationale. The form does not turn subjective ratings into a prediction.
Does this include cybersecurity?
It can record interfaces with electronic access or CCTV systems, but a separate IT security assessment is needed for cyber risks.
Should detailed security weaknesses be shared publicly?
No. Follow your organisation access and information-handling controls when storing or distributing the report.
What are the limits of this template?
This records site-specific judgments. It is not a certification, police approval or an automated prediction of crime, and it does not replace an IT security audit.
Can I complete this form on site and share the record?
In the SiteSurvey app the form works offline, with signatures recorded against the questions. Share the completed record as a PDF or a link. Dates and action owners are recorded fields; this form does not send reminders or update other systems.
Related
Related templates
Templates that go with the physical security risk assessment form
A security patrol record covering the assigned route, timed checkpoint observations, access restrictions, incidents, escalation and shift handover.
An access control service record covering authorised scope, door hardware, approved functional checks, event evidence, defects and secure handover.
An intruder alarm service record covering system scope, authorised tests, detector and power observations, faults, restoration and customer handover.
Use this physical security risk assessment form with your team
Add it from the form library in one click, change any question, and every completed form becomes a branded PDF report.
Start your trial →