Form library · Quality and compliance
IT risk assessment template
For people assessing risks to an IT service. Record scope and method, risk scenarios and assurance and review. Try the form below, see every question or download a blank PDF or Word copy.
Ready to use from the form library, and every question is yours to edit. Trial from £1, cancel any time.
Try it on your phone
Try it on this phone
Fill in the IT risk assessment on your phone now
See how the IT risk assessment looks on your phone
Scan the code with your phone camera. It opens the real form, no sign-up needed.
Open the live example and fill it in, just as your team would on site. No sign-up needed.
See it on this phoneEvery question is editable. Add this form to your account, then change the wording, add or remove questions and options, and make it fit your own jobs.
How should cyber risks be assessed?
NCSC recommends choosing an approach that helps the organisation understand its actual cyber risks. Its framework considers context, decision makers, risk analysis, communication, implementation and review; no single method suits every situation.
Last updated . Facts checked by the SiteSurvey team on 6 October 2026 against NCSC cyber risk management and NCSC cyber risk management framework.
Try the IT risk assessment form live
Answer a few questions and watch it adapt. Your answers are not saved, and any photos you add are deleted within the hour.
This is the real form as your team would use it: questions appear as you answer, scores work themselves out and you can add photos and signatures. No sign-up needed.
Want to see one filled in? See a completed IT risk assessment report (PDF), made by SiteSurvey from a fictional site visit.
Fill it in on a phone or tablet
Your team completes the it risk assessment on site in the SiteSurvey app on iPhone, iPad and Android phones and tablets. The project name and address fill in for them, it works without signal, and it syncs when the device is back online with photos kept against the question they answer.
Customers and subcontractors do not need the app: send them a link and they can fill it in from any browser.
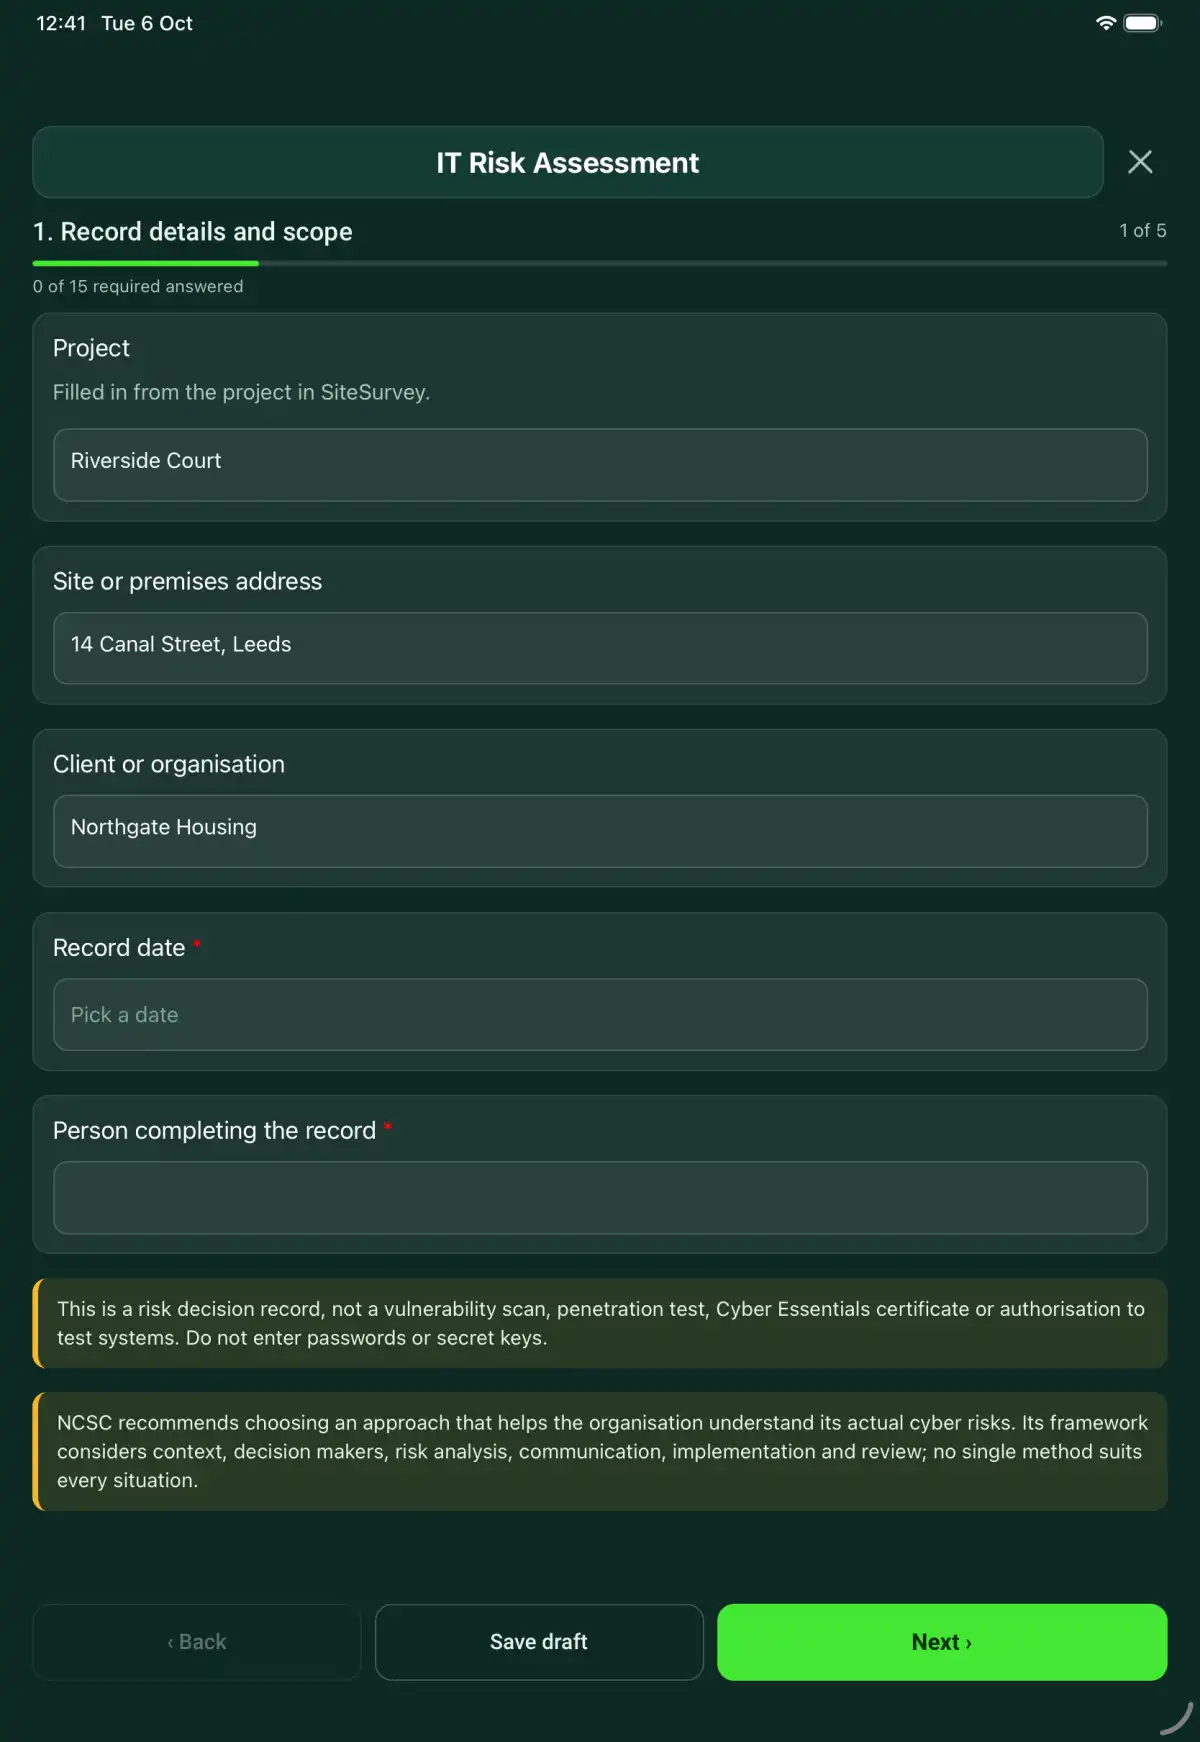
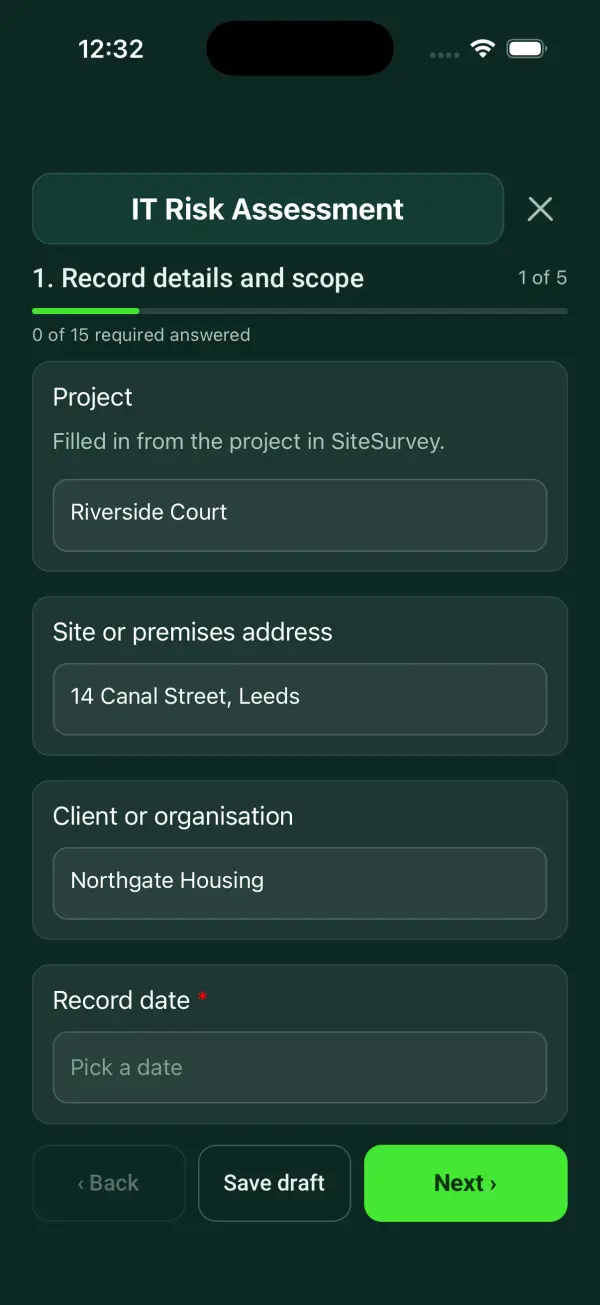
Every question in the IT risk assessment template
An IT risk assessment linking business services, threat scenarios, existing controls, treatment decisions, accountable owners and review evidence. 5 sections and 33 questions. Follow-up questions and guidance appear only when an answer calls for them, so the person on site never sees the ones that do not apply.
Make it your own: every question is editable
This is a starting point, not a fixed form. Once it is in your SiteSurvey account you can reword any question, add or remove questions, sections and answer options, and add your own logo, so it fits the way your team works and the jobs you do.
Details you only enter once
Add this form to a project in SiteSurvey and it fills in what the project already knows, so nobody on site retypes it and every form on the job uses the same names. Anything filled in can still be changed.
- Project: the project name
- Site or premises address: the site address, from the space or the project
- Client or organisation: the project's customer
Record details and scope
- ProjectShort answer
Filled in from the project in SiteSurvey.
Fills in from the project name - Site or premises addressShort answerFills in from the site address, from the space or the project
- Client or organisationShort answerFills in from the project's customer
- Record date*Date
- Person completing the record*Short answer
- CheckThis is a risk decision record, not a vulnerability scan, penetration test, Cyber Essentials certificate or authorisation to test systems. Do not enter passwords or secret keys.
- CheckNCSC recommends choosing an approach that helps the organisation understand its actual cyber risks. Its framework considers context, decision makers, risk analysis, communication, implementation and review; no single method suits every situation.
Scope and method
- Business service and system boundary*Short answer
- Service owner and risk decision maker*Short answer
- Key information, suppliers and dependenciesNotes
Name the systems, suppliers and information the service depends on. Identify which dependencies have evidence and which are assumed.
- Risk method, scale and acceptance policy*Short answer
Risk scenarios
- Cyber riskRepeat for each cyber risk. Each one asks:
- Threat event and affected service*Short answer
- Exposure, weakness and evidence*Notes
- Business consequences*Notes
- Existing controls and assurance evidenceNotes
- Likelihood assessment and basisShort answer
- Risk priority using the stated methodShort answer
- Treatment decision*Choose one
- Reduce
- Avoid
- Share
- Accept
- Pending decision
- Treatment or acceptance rationale*Notes
- Accountable risk owner*Short answer
Assurance and review
- How controls will be checked*Notes
- Next review dateDate
- Changes or incidents that trigger reassessmentNotes
- Authorised acceptance or treatment approval referenceShort answer
Actions and review
- Are further actions required?*Choose one
- Yes
- No
- Further actionRepeat for each further action. Each one asks:Shown when “Are further actions required?” is “Yes”
- Action and evidence reference*Notes
- Person responsible*Short answer
- Target dateDate
- Action status*Choose one
- Open
- In progress
- Completed
- Completion evidence*NotesShown when “Action status” is “Completed”
- Outstanding limitations and information to pass onNotes
- Record status*Choose one
- Ready for review
- Further work needed
- Work or use stopped
- Reviewed byShort answer
- Review dateDate
- Author signature*Signature
- CheckSigning records the information entered. It does not itself certify legal compliance, remove a limitation or authorise unsafe work.
Scope and responsibility
This is a risk decision record, not a vulnerability scan, penetration test, Cyber Essentials certificate or authorisation to test systems. Do not enter passwords or secret keys.
What a useful entry looks like
Key information, suppliers and dependencies
Name the systems, suppliers and information the service depends on. Identify which dependencies have evidence and which are assumed.
Booking service depends on the identity provider and internet connection. Recovery arrangements for the external provider require confirmation.
Fictional example of record wording. Use the actual evidence and approved arrangements for your job; this is not a completed report or an instruction to carry out the work.
See it filled in
A completed IT risk assessment report, made by SiteSurvey from a fictional site visit: every answer, the photos, the guidance that applied and the sign-off, ready to send as a PDF.
IT Risk Assessment FAQs
How should I record “Key information, suppliers and dependencies”?
Name the systems, suppliers and information the service depends on. Identify which dependencies have evidence and which are assumed.
How is this different from the IT security audit?
The audit checks controls. This records business risk scenarios and decisions about treatment, ownership and acceptance.
Is a numerical risk score automatic?
No. Record the organisation’s method and reasoning; the form does not turn uncertain estimates into a default score.
Can it run a vulnerability scan?
No. It only records findings and evidence references from separately authorised work.
What are the limits of this template?
This is a risk decision record, not a vulnerability scan, penetration test, Cyber Essentials certificate or authorisation to test systems. Do not enter passwords or secret keys.
Can I complete this form on site and share the record?
In the SiteSurvey app the form works offline, with signatures recorded against the questions. Share the completed record as a PDF or a link. Dates and action owners are recorded fields; this form does not send reminders or update other systems.
Related
Related templates
Templates that go with the IT risk assessment form
A business continuity record covering critical services, disruption triggers, recovery priorities, dependencies, communications and exercise findings.
An event risk assessment covering setup, public opening and breakdown, crowd movement, contractors, weather, emergency arrangements and review.
Use this IT risk assessment form with your team
Add it from the form library in one click, change any question, and every completed form becomes a branded PDF report.
Start your trial →